SHARED INFRASTRUCTURE.
Common infrastructure should support fair access, secure interoperability, and participation by multiple qualified providers.
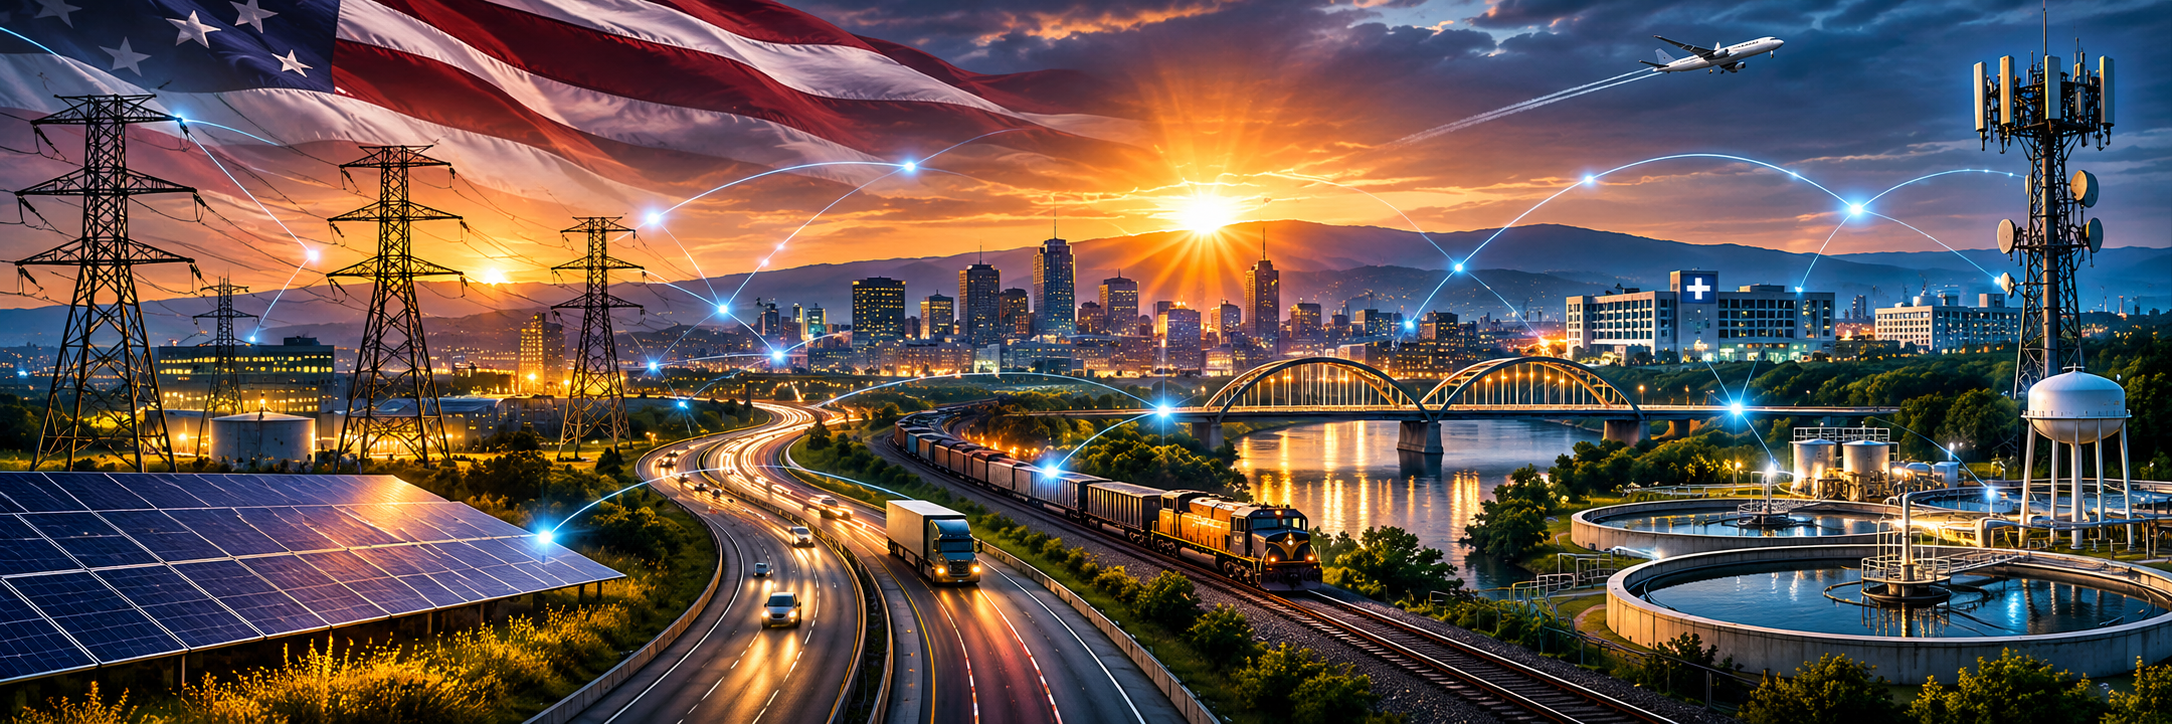
America's future must not depend on who controls the infrastructure. It must depend on how resiliently we engineer it. By enabling shared access, independent operation, secure interoperability, and meaningful competition, we can build essential systems that serve the entire nation.
Common infrastructure should support fair access, secure interoperability, and participation by multiple qualified providers.
Independent governance, alternative operating paths, and accountable decision-making reduce concentrated risk and avoidable single points of failure.
Reliable infrastructure and meaningful competition can expand opportunity for families, small businesses, innovators, and communities across America.
THE STRENGTH OF A NATION IS NOT MEASURED BY HOW MUCH INFRASTRUCTURE ONE ORGANIZATION CONTROLS, BUT BY HOW MANY PEOPLE BENEFIT FROM WHAT WE BUILD TOGETHER.
America's infrastructure is not a collection of isolated assets. Energy, communications, water, healthcare, transportation, supply chains, emergency services, and digital systems depend on one another. Understanding those relationships is the first step toward engineering resilience.
Shared infrastructure must make these systems more capable without making them dependent on a single provider, operator, platform, or point of control. Interconnection must be deliberate. Independence must be preserved.
Select any infrastructure sector to explore its dependencies, downstream impacts, and engineering safeguards.
Conceptual relationship model. Actual dependencies and failure pathways vary by region, asset, and operator. The shared layer represents interoperable capabilities, not a centralized controller.
Electricity and fuel systems support nearly every other essential service. Their resilience depends on secure operations, physical assets, supply chains, and recovery capability.
Fuel and generation resources, control systems, communications, equipment, workforce, and logistics.
Water treatment, hospitals, communications, transportation, businesses, and households.
Independent backup power, sectional isolation, secure controls, diversified resources, and tested restoration procedures.
Consider a hypothetical regional power disruption. If backup capabilities, communications, and operational dependencies are not independently protected, the original disruption can create additional service failures.
This is an illustrative failure pathway, not a prediction of an inevitable cascade. Properly engineered safeguards can interrupt the sequence at multiple points.
Design common capabilities, secure interfaces, and fair-access arrangements that enable multiple qualified participants without requiring exclusive dependence on one provider.
Maintain security boundaries, operational autonomy, and independent recovery options. A failure in one organization must not automatically become a failure across the entire network.
Validate interoperability, failure containment, backup independence, and restoration under realistic conditions. Shared infrastructure must be measured by demonstrated resilience.
The purpose of national resilience architecture is to make cooperation a strength, not a vulnerability. Shared capabilities should expand opportunity while independent safeguards preserve continuity.
National resilience cannot depend on one technology, one provider, or one organization. It must be engineered across multiple complementary layers, each with defined responsibilities, independent safeguards, and measurable performance.
The following conceptual architecture organizes resilience into four engineering layers. These are complementary functions, not a mandatory technology stack or a centralized national control system.
A practical framework for connecting shared capabilities while preserving independent operations and recovery.
Assets, facilities, networks, equipment, energy, and essential service capacity.
Standards, interfaces, trusted exchanges, and controlled cross-system coordination.
Local autonomy, segmented control, continuity capabilities, and independent recovery.
Testing, monitoring, measurement, accountability, and verified improvement.
Engineered for continuity. Designed for participation. Measured by results.
Conceptual engineering model. The four layers operate together and reinforce one another; they do not imply a single national command structure.
The physical foundation includes the facilities, networks, equipment, and resources required to deliver essential services.
ENGINEERING CONTROLSShared infrastructure requires systems to exchange information and coordinate safely without creating unrestricted access or dependence on a single platform.
ENGINEERING CONTROLSOperators must retain the ability to sustain critical functions, isolate disruptions, and restore services even when shared dependencies are unavailable.
ENGINEERING CONTROLSResilience must be demonstrated through evidence, not assumed from documentation, technology purchases, or policy statements.
ENGINEERING CONTROLSShared infrastructure succeeds when it expands access and cooperation without forcing every participant to surrender control of essential operations.
Physical corridors, network interconnection, technical standards, compatible interfaces, infrastructure capacity, situational information, and coordinated recovery resources— where safe, practical, and appropriate.
Operational authority, security boundaries, sensitive information, essential recovery capabilities, independent decision-making, and the ability to continue critical functions when a shared service fails.
Verify that disruptions remain within defined boundaries rather than spreading unnecessarily across connected services and organizations.
Demonstrate that essential functions can continue through alternative resources, local operating modes, and protected recovery paths.
Measure recovery time, restoration completeness, operational readiness, and the effectiveness of corrective improvements.
Shared infrastructure creates opportunity. Distributed control protects continuity. Continuous assurance proves that the architecture performs as intended.
No infrastructure system can guarantee that every component, connection, supplier, or operator will always perform perfectly. Resilient architecture begins by acknowledging that disruptions occur and engineering systems to withstand them.
The goal is not to eliminate every possible failure. It is to prevent an isolated disruption from becoming an unnecessary regional or cross-sector crisis.
Establish boundaries that prevent a disruption from spreading into otherwise functioning systems.
Avoid relying on alternatives that share the same hidden vulnerability or failure point.
Preserve essential functions even when full service capacity cannot be maintained.
Restore operations through verified resources, procedures, and alternative pathways.
Compare two conceptual designs facing the same hypothetical disruption. The difference is not whether a failure occurs. The difference is whether safeguards contain its consequences.
In this hypothetical design, four essential services depend on a shared power source without sufficiently independent backup capabilities.
Without independent safeguards, one failure can interrupt multiple essential services. This illustrates a possible failure pathway, not an inevitable outcome.
Segment electrical, digital, communications, and operational systems so that a fault in one area does not automatically compromise another.
Verify that backup systems do not share the same vulnerable power source, communications route, location, credentials, or critical supplier.
Identify the minimum essential functions that must continue. Engineer controlled operating modes that preserve those functions when capacity is constrained.
Exercise restoration procedures, validate backup resources, measure recovery objectives, and confirm that systems can return to service safely.
Consider a hypothetical community experiencing an extended utility power interruption. The architecture determines which essential functions can continue and how quickly full service can be restored.
A facility has a backup generator, but its fuel resupply depends on unavailable transportation. Its monitoring depends on a communications provider affected by the same outage. Its recovery plan assumes resources that cannot be accessed.
Essential loads are prioritized. Backup power capacity and fuel arrangements are validated. Alternative communications are available. Operators have tested procedures for reduced-capacity operation and staged restoration.
What happens when our primary dependency becomes unavailable?
Are our backup capabilities genuinely independent?
Which essential functions must continue during disruption?
Can operators maintain control without the normal digital systems?
Have we tested failure containment under realistic conditions?
Can we demonstrate safe, timely, and complete recovery?
We cannot engineer a world without disruption. We can engineer systems that contain failure, preserve essential services, and recover with greater independence, confidence, and accountability.
A resilient nation cannot depend on a single organization to operate, coordinate, or restore every essential service. National continuity must emerge from capable local systems, cooperative regional networks, and interoperable national resources.
The objective is not to centralize control. It is to create the conditions in which independent operators can cooperate, share appropriate resources, and maintain essential services during disruption.
A conceptual federated architecture: local capability, regional cooperation, national interoperability, and coordinated recovery.
Compatible interfaces, information exchange, mutual assistance frameworks, resource visibility, and cross-region coordination without a single national operating controller.
Shared resources, reciprocal assistance, and coordinated restoration.
Independent operators, alternative capacity, and interoperable services.
Mutual support, resource coordination, and recovery readiness.
Illustrative governance and coordination model—not a depiction of an existing national operating network or a proposal to transfer operational authority.
Select a hypothetical disruption to see how local, regional, and national capabilities can work together while preserving appropriate operational authority.
A community experiences a localized essential-service interruption. The affected operator activates its continuity procedures and requests assistance if needed.
Local operators isolate the disruption, protect essential functions, and begin restoration.
Neighboring organizations may provide personnel, equipment, or alternative capacity through established assistance arrangements.
Shared standards and coordination mechanisms can support communication and resource exchange when wider assistance becomes necessary.
Resolve the disruption at the lowest effective operational level while maintaining access to additional support if required.
Operators remain responsible for their systems, safety boundaries, operating procedures, and recovery decisions, subject to applicable laws, regulations, and emergency authorities.
Compatible standards, transparent participation, mutual-aid arrangements, and secure information exchange enable organizations to cooperate without relying on one controlling platform.
Critical operators should maintain tested recovery procedures and essential resources that do not depend entirely on external coordination systems.
Establish clear roles, authorization boundaries, escalation procedures, resource commitments, and evidence-based performance expectations.
A national continuity architecture should make meaningful participation possible for communities and organizations of different sizes. The benefits of secure interoperability should not be reserved exclusively for those with the greatest resources.
Accessible standards, competitive service options, and continuity resources can help smaller enterprises participate without unnecessary dependence on a single provider.
Shared capacity, alternative connectivity, cooperative arrangements, and practical recovery planning can expand options where infrastructure resources are limited.
Interoperable interfaces, transparent participation requirements, and fair competition can create opportunities for qualified organizations to contribute new solutions.
A continuity model must be evaluated through observable performance, tested coordination, and demonstrated recovery capability.
Which priority services remain available during a disruption?
How quickly and completely can affected operations be safely restored?
Can critical functions continue when external dependencies are unavailable?
Have organizations tested interoperability, mutual assistance, and escalation?
Local capability. Regional cooperation. National interoperability. Shared resilience. An architecture designed to strengthen every community without concentrating unnecessary control.
Infrastructure can be technically resilient and still be vulnerable to concentrated control, opaque decision-making, unfair access, or inadequate oversight. Engineering national resilience requires governance that protects the public interest as deliberately as the architecture protects essential services.
Shared infrastructure must operate under clear rules, defined responsibilities, transparent participation requirements, independent verification, and enforceable accountability.
Establish transparent, objective participation requirements that do not unnecessarily exclude qualified competitors, small businesses, or communities.
Define who may make decisions, operate systems, authorize changes, and initiate recovery. Avoid unnecessary concentration of operational power.
Use qualified, appropriately independent review to assess compliance, security, resilience, and adherence to established rules.
Favor documented, secure interfaces and portable capabilities that support compatibility and reduce unnecessary vendor lock-in.
Evaluate performance through testing, evidence, defined recovery objectives, and corrective action rather than relying on unsupported assurances.
Document obligations, escalation procedures, remedies, reporting duties, and appropriate consequences when commitments are not fulfilled.
Select a governance responsibility to explore how decision-making, verification, and accountability should be separated.
Participation in shared infrastructure should be governed by transparent, objective requirements appropriate to the service and its risks.
Authorized infrastructure owners or governing bodies apply documented access and participation rules.
Independent or appropriately separated reviewers evaluate whether requirements are applied consistently.
Responsible decision-makers must document decisions and provide appropriate review or appeal mechanisms.
The following illustrative responsibility model separates operational control, shared coordination, and independent assurance. Actual assignments must reflect ownership, contracts, jurisdiction, and applicable law.
| RESPONSIBILITY | PRIMARY AUTHORITY | ACCOUNTABILITY MECHANISM |
|---|---|---|
| Local system operations | Authorized system owner or operator | Operating procedures, access controls, and documented performance |
| Shared infrastructure access | Infrastructure owner or designated governing body | Published criteria, consistent application, and review mechanisms |
| Interoperability standards | Appropriate standards bodies and participating stakeholders | Transparent development, documented specifications, and conformance testing |
| Incident response | Responsible operators and applicable authorities | Defined escalation, incident records, and after-action review |
| Recovery coordination | Authorized operators and agreed coordination partners | Mutual-aid agreements, recovery exercises, and restoration evidence |
| Independent assurance | Qualified reviewers with appropriate independence | Evidence-based findings, corrective action tracking, and follow-up verification |
Conceptual allocation of responsibilities—not a replacement for existing regulatory authority, legal obligations, or established emergency management structures.
A declaration of resilience is not proof of resilience. Governance must require appropriate testing, transparent reporting, documented findings, and verified remediation.
Validate security boundaries, interoperability, dependency independence, failure containment, and recovery capability against defined requirements.
Test realistic disruption scenarios involving operators, suppliers, regional partners, and essential service dependencies.
Publish appropriate performance measures and governance outcomes while protecting sensitive infrastructure details, security information, and personal data.
Track deficiencies, assign responsible owners, establish remediation deadlines, and verify that corrective measures actually work.
Some infrastructure is necessarily shared because of physical, economic, or operational realities. The engineering challenge is to make that shared capacity accessible and accountable without allowing avoidable concentration of control.
A single provider controls essential interfaces, restricts interoperability, creates unnecessary switching barriers, or becomes the only practical recovery path. Participants may then inherit dependencies they cannot independently evaluate or manage.
Transparent access rules, documented interfaces, portable capabilities, independent operating boundaries, competitive participation where feasible, and meaningful review mechanisms reduce avoidable concentration risk.
Are requirements objective, transparent, and consistently applied?
Are operational powers limited, documented, and appropriately separated?
Is performance verified by qualified reviewers with appropriate independence?
Are obligations, escalation paths, remedies, and corrective actions clearly defined?
The architecture must protect not only the continuity of essential services, but also the independence, opportunity, and accountability of those who build, operate, and depend on them. Governance is not an afterthought. It is part of the engineering.
We have the engineering knowledge to build more resilient systems. We have the technology to connect them securely. We have the opportunity to expand participation, protect independence, and strengthen essential services. What remains is the discipline to turn architecture into action.
A national resilience architecture must move beyond diagrams, policy statements, and technology promises. It must become a practical, testable, accountable approach to improving the infrastructure communities depend upon.
Implementation should begin with real dependencies, measurable continuity requirements, qualified participants, and demonstrable results. Build what can be verified. Improve what can be measured. Expand what has proven effective.
Identify essential services, critical assets, shared dependencies, operational boundaries, and potential failure pathways.
Define secure interfaces, independent operating modes, diversified resources, failure containment, and recovery requirements.
Test interoperability, dependency independence, operational resilience, and restoration performance under realistic conditions.
Introduce proven capabilities through phased implementation, defined responsibilities, measurable objectives, and controlled change.
Verify results, correct weaknesses, share appropriate lessons, and scale successful approaches without sacrificing independence.
Prioritize continuity for the infrastructure that sustains public safety, healthcare, energy, water, communications, transportation, and economic activity.
Enable secure cooperation without requiring every operator to depend on a single controlling organization, technology, or recovery pathway.
Support transparent access, interoperable standards, and meaningful opportunities for qualified businesses, infrastructure providers, and communities of different sizes.
Measure resilience through tested continuity, independent recovery, accountable governance, and demonstrated improvements in essential service protection.
National resilience is not an achievement reserved for a few large organizations. Its purpose is to strengthen the communities, businesses, essential services, and people who depend on infrastructure every day.
Greater continuity, recovery capability, and access to essential services.
More opportunities to participate, compete, and operate resiliently.
Secure cooperation, defined responsibilities, and stronger operational safeguards.
Stronger economic continuity, greater adaptability, and reduced systemic risk.
Shared infrastructure. Distributed control. Independent operations. Accountable governance. A stronger foundation for national resilience and shared prosperity.
We believe America's essential infrastructure should be secure, resilient, interoperable, and engineered to serve the people who depend on it. The path forward begins with better design, stronger safeguards, and the commitment to make resilience real.